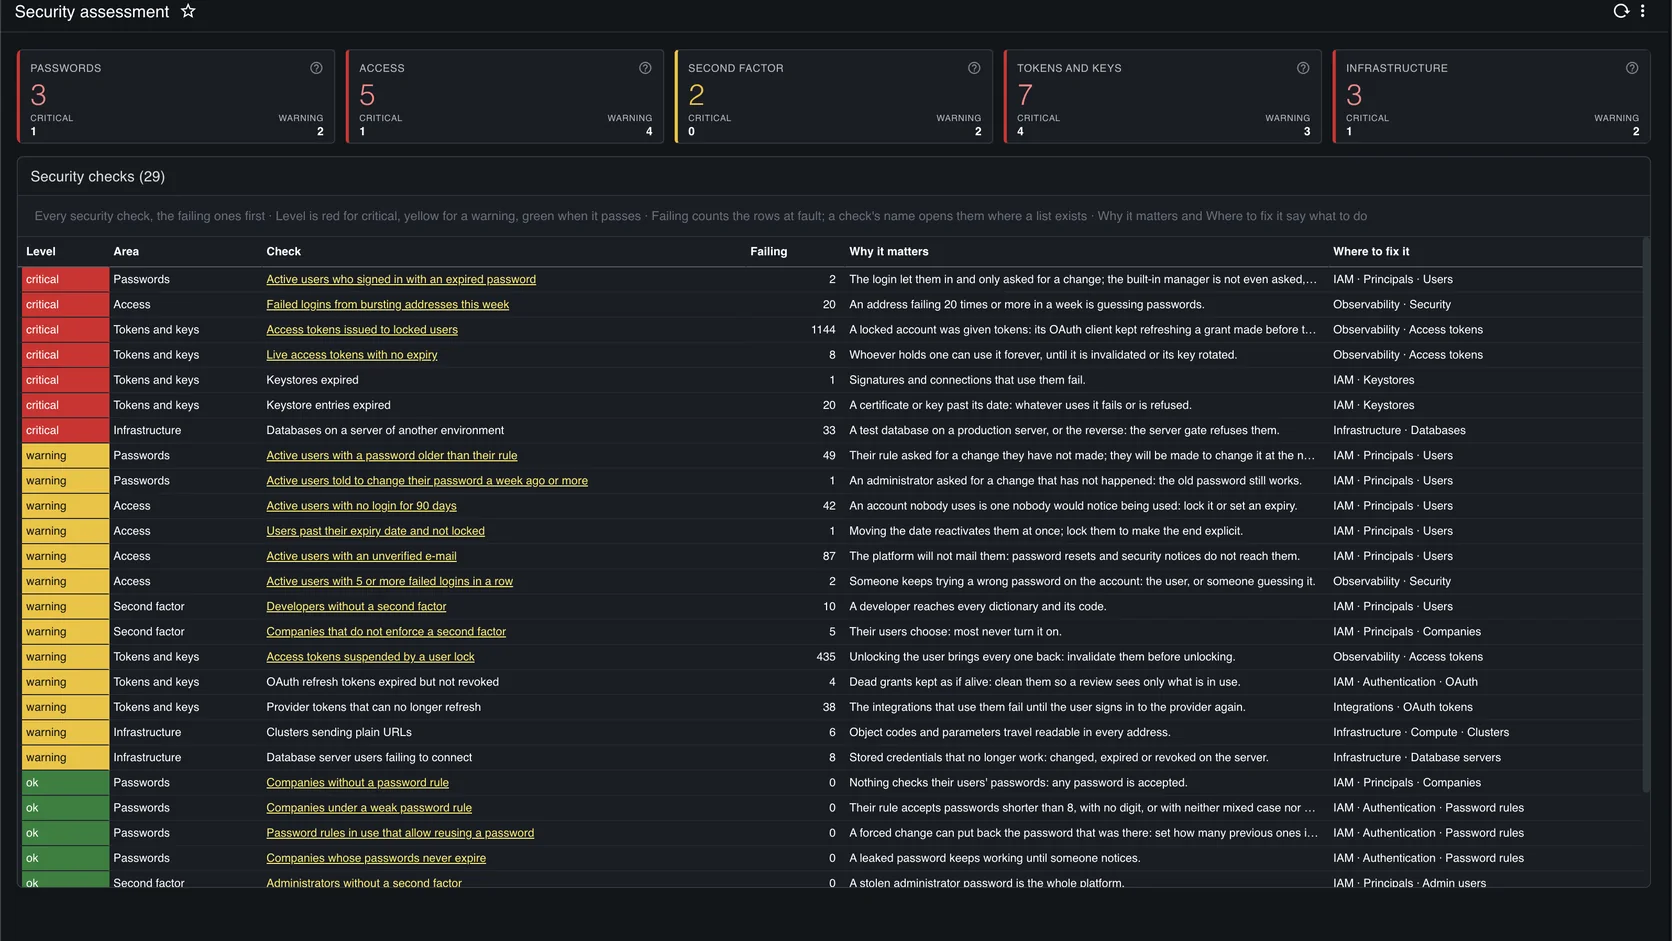
The failed-login table held one row per wrong password on the login form and nothing else. A locked account's client refusing on every refresh, or a script retrying a wrong password, left either no row or a row per attempt. This release records all of it, and records a storm as a storm.
Recorded
- Three doors, one recorder A refused JWT, a refused token request and a failed form login all go through the same recorder, with the method named.
- Storm control The first failure for a user, method and address is written at once; repeats are counted in memory and written as one row with the count when the minute closes. At most 10,000 keys are held, and a key past the cap is counted and reported rather than lost.
- Counted, not rowed Every figure, from the security tile to the rankings by address and user, sums the count, so a storm reads its real size.
Told
- At the next sign-in A notifier sums the unseen attempts and files one warning through the user's own handler, in five languages. It replaces a cron task that polled every two minutes, 720 runs a day, for a notice the user could only read after signing in anyway.
The companies page and the risk markers of the same week read these counts. A user failing to log in is a High mark, in red, on the first screen an administrator opens.